Challenge overview
The “Ben 10” challenge presents a web application themed around Ben Tennyson’s Omnitrix, featuring hidden credentials and an access control vulnerability. The objective is to exploit these weaknesses to retrieve a flag.
Analysis
The challenge provides:
- a web application at
http://ben10.challs.srdnlen.it:8080 - a hint about a mysterious “Materia Grigia” form hidden in the system
During account creation, the application contains a hidden HTML element with admin credentials:
<!-- secret admin username -->
<div style="display:none;" id="admin_data">admin^victim99^a6b0fc68a1</div>
This reveals:
- username format:
admin^USERNAME^a6b0fc68a1 - account identifier pattern using
^as a delimeter
Exploitation
- Account creation
- create a regular user account
- note the default password pattern using something like
victim:victim
- Password reset exploitation
- initiate password reset for your regular account
- capture the reset token
- use the same token with the hidden admin username
admin^victim99^a6b0fc68a1 - submit to
/forgot_passwordendpoint
- Admin access
- login with the admin credentials
- navigate to view
ben10.webp - retrieve flag
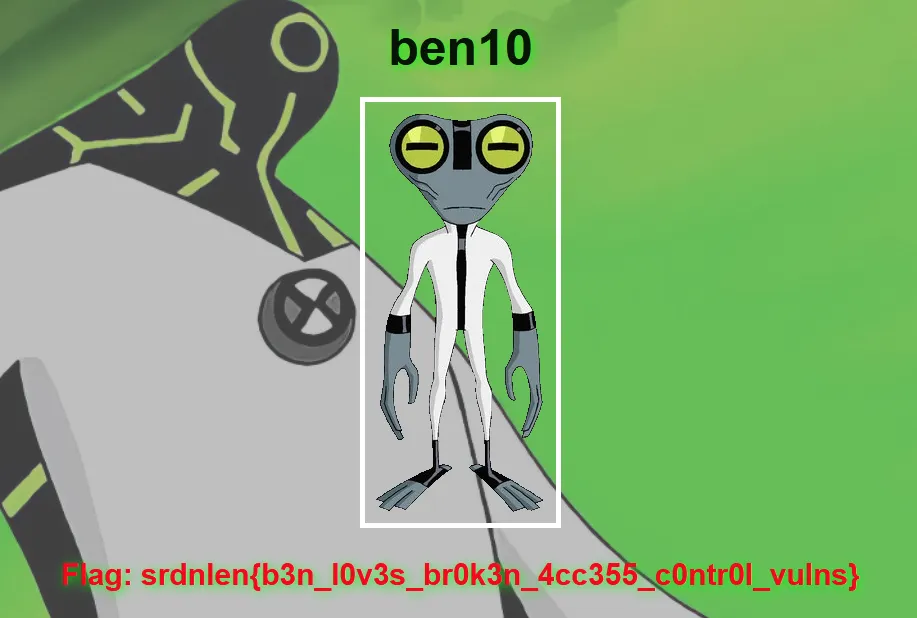
Flag:
srdnlen{b3n_l0v3s_br0k3n_4cc355_c0ntr0l_vulns}
Key takeaways
- IDOR - application allows password reset tokens to be reused across accounts and no proper validation of token ownership.
- Information Disclosure - Hidden HTML elements expose sensitive admin credentials.
- Access Control - Lack of proper access control in password reset functionality.
This post is licensed under CC BY 4.0 by the author.